Executive Overview
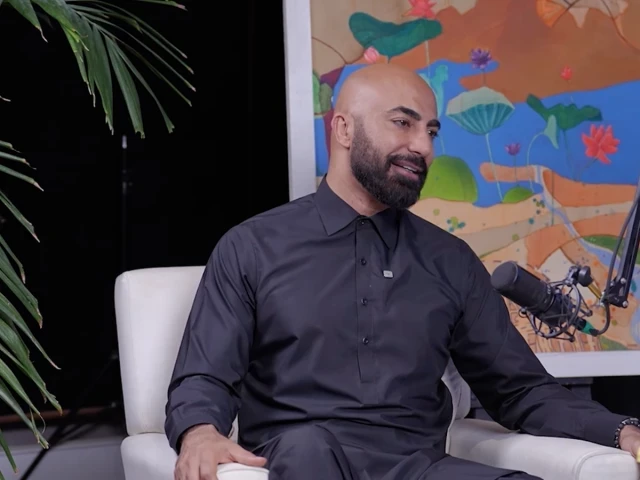
In an era where personal and professional lives are inextricably linked to digital devices, the vulnerability of high-profile figures to cyberattacks has become a pressing global concern. Pakistan’s celebrated fashion icon, Hassan Sheheryar Yasin—widely known simply as HSY—has become the latest high-profile victim of a sophisticated cyber intrusion. On October 20, the designer’s digital infrastructure was severely compromised, leaving his primary smartphone device, WhatsApp account, email addresses, and comprehensive contact list exposed to unauthorized third parties.
The security breach, which has sent shockwaves through the South Asian fashion and entertainment industries, prompted HSY to issue an immediate and urgent public advisory via his official social media channels. With hundreds of contacts reportedly receiving suspicious communications in the immediate aftermath of the hack, the incident underscores the dangerous mechanics of modern social engineering and account takeover (ATO) attacks. Cybercriminals frequently target high-net-worth individuals and public figures to exploit their networks, utilizing trusted identities to perpetrate financial fraud, distribute malware, and harvest sensitive personal data.
This comprehensive report examines the anatomy of the security breach experienced by HSY, detailing the chronology of the event, the potential vectors and risks associated with such targeted cyberattacks, and the broader context of digital security vulnerabilities facing public figures today. Furthermore, this article provides a deep dive into the official statements released by the designer, analyzes the preventative measures necessary to mitigate such threats, and offers a forward-looking perspective on how celebrities and digital users alike can better safeguard their interconnected digital ecosystems against increasingly advanced cyber threats.
Read Also
Detailed Chronology of the Breach
The unfolding of the cyberattack against HSY was swift, catching both the designer and his associates off guard. While the exact technical vector of the breach remains under investigation by cybersecurity specialists, the timeline of events highlights how quickly digital infrastructure can be weaponized once compromised.
The Point of Compromise: October 20
The security incident materialized on October 20, when unauthorized actors successfully bypassed the security protocols protecting HSY’s primary mobile device and core communication channels. According to statements released by the designer, the breach was total, affecting not just a single application but an interconnected web of personal and professional communication tools.
Within a remarkably short window, the attackers gained access to:
- The Primary Smartphone Device: Giving the perpetrators potential control over device-level functions and two-factor authentication (2FA) tokens.
- WhatsApp Account: The primary messaging platform used extensively for both personal correspondence and professional collaborations within the fashion industry.
- Email Accounts: Serving as the central repository for business negotiations, confidential designs, and sensitive personal documentation.
- The Global Contact List: A high-value asset containing hundreds of names, phone numbers, and email addresses of celebrities, corporate partners, media personalities, and close friends.
The Immediate Aftermath and Broadcast Phase
Once inside the ecosystem, the perpetrators wasted little time in leveraging the compromised accounts. Exploiting the inherent trust that contacts place in a known identifier, the malicious actors began broadcasting messages to hundreds of individuals within HSY’s address book.
In modern account takeover scenarios, these messages typically follow established social engineering playbooks. Attackers often pose as the account holder experiencing an emergency, requesting immediate financial assistance via wire transfer or digital wallets, or alternatively, distributing malicious links masked as shared photographs, media files, or verification prompts. By the time HSY and his technical team recognized the anomaly and initiated containment protocols, a significant portion of his network had already received the unauthorized communications.
Containment and Recovery Operations
Upon discovering the breach, HSY and his technical support team initiated immediate damage-control procedures. The priority shifted from passive observation to aggressive containment—revoking session tokens, attempting to recover administrative control over the compromised email and messaging portals, and drafting an emergency broadcast to halt the spread of fraudulent messages.
While recovery efforts remain ongoing, the primary focus has centered on severing the attackers’ access pathways and ensuring that the corrupted endpoints are thoroughly sanitized or replaced. Despite the chaos of the breach, HSY moved swiftly to stabilize the situation and publicly alert his community before the fraudulent communications could inflict widespread financial or reputational damage.
Supporting Context & Metrics: The Anatomy of Account Takeovers
The cyber incident involving HSY is not an isolated event; rather, it reflects a booming, highly lucrative global cybercrime economy built around Account Takeovers (ATOs) and social engineering. Understanding the mechanics and scale of these attacks provides critical context for why such breaches occur and how dangerous they can be.
The Rise of Mobile and Messaging Exploits
In contemporary society, smartphones serve as the ultimate master keys to our digital lives. Through single sign-on (SSO) frameworks and SMS-based two-factor authentication, gaining control of a physical phone or a primary phone number often grants a cascading level of access to linked cloud storage, social media profiles, and financial applications.
According to global cybersecurity research, attacks targeting messaging applications like WhatsApp have surged exponentially. Cybercriminals frequently employ advanced techniques such as:
- SIM Swapping: Manipulating mobile network operators to transfer a victim’s phone number to a SIM card controlled by the attacker, thereby intercepting SMS-based verification codes.
- Phishing and Social Engineering: Tricking targets into revealing their registration codes or clicking malicious links that install spyware or remote access trojans (RATs) onto the device.
- Credential Stuffing: Utilizing automated scripts to test leaked username and password combinations across multiple platforms, exploiting the common human habit of reusing passwords.
The Vulnerability of Public Figures
Celebrities, designers, and public intellectuals are prime targets for cybercriminals for several distinct reasons:
- High-Trust Networks: A message originating from a celebrated designer like HSY carries an inherent level of authority and trust, making recipients significantly more vulnerable to social engineering ploys compared to messages from unknown numbers.
- Lucrative Connections: A public figure’s contact list is essentially a curated directory of affluent individuals, business executives, and fellow celebrities who may possess greater financial resources or valuable corporate secrets.
- Reputational Leverage: Threat actors frequently leverage the threat of public embarrassment or the release of private communications to extort public figures, though in many cases, the primary goal remains financial fraud perpetrated against the victim’s network.
Official Statements and Public Advisory
Recognizing the gravity of the situation and the potential harm facing his associates, HSY issued a direct, transparent, and comprehensive public advisory via his official Instagram account. Eschewing generic public relations language, the designer opted for a candid breakdown of the breach, explicit instructions for his contacts, and a reassuring message regarding his personal safety.
The Instagram Statement: A Breakdown
In his published statement, HSY outlined the precise scope of the breach and issued clear instructions to anyone who might receive communication from his accounts:
"Yesterday, 20 October, my phone, WhatsApp, email and contact list were compromised. I do not know the extent of the messages that may have been sent, but hundreds of people have received messages from my accounts."
By acknowledging that hundreds of individuals had already been targeted, the designer set an immediate tone of urgency. He explicitly warned his community against engaging with any incoming material purporting to come from him:
"Please do not respond to unusual messages, send money or personal information, click links, open attachments, or follow any instructions that appear to come from me without verifying them directly through a trusted number."
Prioritizing Community Safety Over Persona
Cybersecurity experts frequently praise public figures who respond to hacks with radical transparency. By openly admitting that his accounts were weaponized, HSY effectively neutralized a significant portion of the attackers’ leverage. Fraudulent requests rely heavily on the victim’s embarrassment or hesitation to verify claims; by warning his network preemptively, he drastically reduced the likelihood that his contacts would fall prey to financial scams or malware distribution.
Furthermore, HSY took care to address the psychological anxiety such breaches cause among friends, family, and business partners:
"I’m okay, and we’re working to secure everything. I’m truly sorry for any worry, confusion or inconvenience this may have caused."
This empathetic approach helped humanize a technical crisis, transforming a potential public relations nightmare into an opportunity for collective digital vigilance.
Preventative Measures and Digital Best Practices
The breach experienced by HSY serves as a stark wake-up call for professionals across all industries regarding the necessity of robust digital hygiene. Securing modern communication channels requires a multi-layered approach to defense. Cybersecurity professionals recommend implementing the following vital practices to prevent and mitigate Account Takeovers:
1. Implement Advanced Authentication Protocols
- Multi-Factor Authentication (MFA): Enable MFA across all email, social media, and messaging applications. Crucially, prioritize app-based authenticators (such as Google Authenticator or Authy) or hardware security keys over SMS-based verification, which remains vulnerable to interception.
- Passkeys: Where available, adopt passkeys as a phishing-resistant alternative to traditional passwords.
2. Secure Messaging Platforms
- Two-Step Verification on WhatsApp: Activate WhatsApp’s built-in two-step verification feature, which requires a custom PIN whenever a phone number is re-registered on a new device.
- Privacy Settings: Restrict profile visibility, "Last Seen" statuses, and read receipts to minimize the data exposed if an unauthorized party gains peripheral visibility into the application.
3. Establish Verification Protocols
- Out-of-Band Confirmation: If you receive an unusual request—particularly one involving financial transactions, urgent favors, or sensitive data sharing—from a trusted contact, always verify their identity through an independent channel (such as a direct voice call or an alternative communication medium).
- Treat Links and Attachments with Suspicion: Never click on unsolicited links or open compressed attachments sent via messaging apps, even if they appear to originate from close friends or colleagues whose accounts may have been quietly compromised.
Future Outlook: The Evolving Landscape of Digital Security
As we look toward the future, the intersection of celebrity, commerce, and cybercrime will undoubtedly continue to evolve. The HSY incident highlights a broader societal reality: digital infrastructure is only as secure as its weakest link, and human psychology remains the primary vector exploited by modern threat actors.
The Role of Tech Platforms in Enhanced Protection
Moving forward, technology companies and social media platforms must shoulder greater responsibility in protecting high-profile accounts. Implementing proactive anomaly detection algorithms that flag unusual messaging spikes, rapid geographic logins, and mass contact-list harvesting can help platforms intercept breaches before unauthorized messages reach hundreds of unsuspecting users. Furthermore, streamlined emergency reporting channels must be established to allow public figures to lock down compromised ecosystems instantly.
Increased Industry Awareness
For the fashion, entertainment, and corporate sectors in Pakistan and globally, the HSY cyber breach will likely serve as a catalyst for a serious reassessment of digital security protocols. Agencies, design houses, and public relations firms are increasingly recognizing the need to treat digital asset management with the same rigor traditionally reserved for physical security and financial accounting.
Conclusion
The cyberattack on HSY’s digital accounts is a cautionary tale for the digital age. It demonstrates how swiftly personal convenience can be upended by malicious actors seeking to exploit trusted networks. However, through rapid public disclosure, decisive containment efforts, and an unwavering commitment to transparency, HSY managed to blunt the effectiveness of the attack. As digital threats grow increasingly sophisticated, the lessons learned from this incident—emphasizing vigilance, multi-layered authentication, and out-of-band verification—remain essential armor for anyone navigating our hyper-connected world.

Comments
Facebook App ID not configured. Please add it in the Customizer.